Phishing Training Perth: 5 Defence Tactics for 2026

Phishing training Perth protects WA businesses from costly email scams. Discover 5 essential employee defence strategies to stop breaches today.
Phishing training in Perth combines continuous simulated social engineering campaigns, employee verification protocols, and layered network defence to protect commercial organisations against credential theft, ransomware, and financial fraud.
📌 Executive Summary & Key Technical Takeaways
- Proactive Human Firewall: Effective phishing defence requires continuous, context-driven simulations tailored to Western Australian commercial supply chains, not one-off compliance tick-boxes.
- Robust Physical & Logical Foundations: Technical barriers require certified Cat5E or Cat6 Ethernet cable, business-grade firewalls, DNS filtering, and hardened network endpoints to intercept malicious ingress points.
- Dual-Engine Model: Unifying ICT Services with commercial electronic security (Commercial CCTV and Access Control) under a Single Point of Accountability eliminates vendor finger-pointing during an incident.
- Verification Over Trust: Combining Multi-Factor Authentication (MFA) with strict out-of-band payment validation processes provides measurable risk mitigation against credential stuffing and whaling.
Table of Contents
Phishing Attacks: A Growing Threat to Commercial Operations
As small business managers and commercial facility operators in Perth, you are juggling complex commercial schedules, regulatory oversight, and tight deadlines. There is an insidious threat that can bring your entire operation to an abrupt standstill in a single, unverified click: an advanced phishing intrusion. The landscape of phishing attacks continues to accelerate in technical complexity, explicitly targeting the commercial engines across Western Australia—from professional service firms in the St Georges Terrace business hub to heavy industrial hubs across Kwinana, Welshpool, and Osborne Park.
While standard IT contractors often focus exclusively on basic antivirus software, our decades of experience architecting integrated systems at Smart SYS demonstrate an indisputable operational reality: your staff act as your primary physical and digital sensory network. However, standard classroom training alone cannot hold the line against automated reconnaissance and social engineering.
This upgraded guide moves past superficial checklists. We explore current attack vectors targeting WA operations, examine why generic off-the-shelf awareness modules fail under pressure, and demonstrate how our unified framework integrates cyber awareness directly with resilient network infrastructure and electronic security controls.
What Exactly is a Phishing Attack?
At its core, a phishing attack is an adversarial form of social engineering—an exploit of identity, authority, and communication protocols. Malicious actors disguise themselves as trusted commercial partners, banking institutions, regulatory entities like the Australian Taxation Office (ATO), or key company directors. Their objective is always to coerce personnel into executing high-risk actions, including:
- Extracting Critical Access Credentials: Uncovering administrative logins, VPN secrets, cloud database credentials, or proprietary customer data.
- Deploying Ransomware & Malicious Payloads: Inducing staff to execute hidden macros, script files, or weaponised attachments that infiltrate local subnets.
- Authorising Fraudulent Financial Transactions: Intercepting vendor supply chains via deceptive billing changes or altered banking disbursement requests.
These exploits are rarely untargeted spam; they leverage automated reconnaissance against Australian commercial registrations and professional networks. The primary variants impacting Perth commercial sites include:
- Email Phishing: Automated, broad-brush distribution campaigns mimicking operational platforms like Microsoft 365, Xero, or Australia Post tracking portals.
- Spear Phishing: Highly customised, researched attacks directed against specific project engineers, financial controllers, or site supervisors, referencing active projects, tender submittals, or local subcontractors.
- Whaling Operations: Precision-targeted manipulation directed at managing directors and C-suite executives to compromise enterprise-tier network authorizations or bypass invoice verification thresholds.
- Smishing (SMS) & Vishing (Voice): Out-of-band social engineering using fraudulent carrier notifications or spoofed voice calls claiming to be internal IT personnel requesting remote desktop credentials.

5 Essential Phishing Defence Tactics for 2026
To defend against increasingly deceptive social engineering, commercial organisations must employ proactive, multi-layered risk mitigation strategies. At Smart SYS, we advise small business managers and commercial facility operators to implement these five non-negotiable tactics:
- Contextual Spear-Phishing Simulations: Discard generic templates. Run recurring simulated phishing tests tailored to the specific software stacks (e.g., Microsoft 365, internal VoIP consoles) and supplier relationships your teams use daily.
- Mandatory Out-of-Band Financial Verification: Enforce strict operational rules requiring any change to vendor bank accounts, payroll details, or major project disbursements to be verified via a second, independently confirmed telecommunications line.
- Zero-Trust Credential Hardening: Roll out phishing-resistant Multi-Factor Authentication (MFA), enforcing hardware tokens or authenticator apps while systematically disabling legacy, unencrypted password authentication protocols across email gateways.
- Structured Network Segmentation: Separate administrative workstations, guest access, and IP-enabled commercial electronic security (Commercial CCTV and Access Control systems) onto isolated VLANs. This contains lateral movement if an endpoint is compromised by a malicious payload.
- Routine Baseline Audits and Gap Analysis: Schedule structured Perth vulnerability assessments that scrutinise both digital network gateways and the physical premises layout to ensure human and technical safeguards are aligned with current operational realities.
The Alarming Reality of Phishing Attacks
Cyber risk across Perth is no longer an abstract concern; it is a recurring reality for local commercial operations. WA’s resource wealth, vibrant commercial construction sectors, and expansive supply chains make our businesses lucrative targets for both international threat syndicates and opportunistic bad actors. The real-world consequences of an uncontained phishing breach run deep:

- Direct Capital Losses: Unauthorised fund transfers and forensic accounting expenditures place substantial strain on cash flow.
- Crippling Operational Outages: Network-wide ransomware triggered by credential theft can lock internal servers, halting field dispatch, job quoting, and client billing for weeks.
- Permanent Commercial Reputation Damage: In Perth’s interconnected business ecosystem, disclosing that client information or tender details have been exfiltrated damages client trust and commercial partnerships.
- Regulatory Non-Compliance Liabilities: Failure to safeguard identity data can trigger formal investigations, breach notification mandates, and severe exposure under statutory Australian privacy frameworks. Review our guidance on how to master Australian data protection & compliance to evaluate your legal exposure.
Why Generic, Off-the-Shelf Training Isn’t the Answer
Off-the-shelf, click-through slide decks from global software portals often fail to protect local organisations. They lack regional and operational context. A generic ten-minute video quiz does not condition an operations manager in Canning Vale to catch a spoofed purchase order referencing actual mining suppliers or regional council planning documents. Effective defence demands continual education, immersive real-world scenarios, and direct alignment with the physical and network infrastructure of your business.
Building a Human Firewall: Our Integrated Approach to Phishing Defence
At Smart SYS, we do not view your staff as systemic vulnerabilities. When equipped with clear guidance and resilient infrastructure, your team becomes an active human sensor network capable of intercepting deceptive communications before payloads trigger.
1. Foundational Training: Beyond the Basics
We instil operational scepticism across departments. Our training regimes condition team members to rapidly spot classic and emerging markers:
- Sender Address Discrepancies: Identifying subtle character substitutions (homoglyphs) in domain names that mimic real vendors or executive staff.
- Fabricated Commercial Urgency: Detecting artificial deadlines designed to short-circuit internal review, such as “Immediate System Cutoff” or “Direct Wire Required.”
- Hyperlink Deception: Inspecting actual destination URLs rather than displayed text to identify proxy landing pages designed to skim user credentials.
- Unscheduled Attachment Deliveries: Identifying unexpected macro-enabled spreadsheets, archive containers (.iso, .zip), or disguised executables.
2. Advanced Simulations Tailored to Western Australian Operations
We design controlled simulated phishing exercises that reflect the day-to-day realities of local commercial enterprises. Instead of generic corporate templates, simulations mirror relevant commercial scenarios, such as regional freight manifests, electronic council notices, or subcontractor invoices. If an employee falls for a simulated bait, the system presents an immediate, non-punitive “teachable moment” highlighting missed indicators. This tactical feedback reinforces learning far better than annual lectures.
3. Incident Escalation & Response Playbooks
Identifying a deceptive email is only half the battle; personnel must execute a standardized, clear response. We assist management in establishing simple, friction-free reporting workflows. By providing a dedicated, single-click mechanism to escalate suspicious items to your managed IT team, a single employee’s vigilance can prompt rapid blacklisting across your entire network boundary.
In-House Project Training in Perth: Delivering Context-Specific Cyber Hygiene
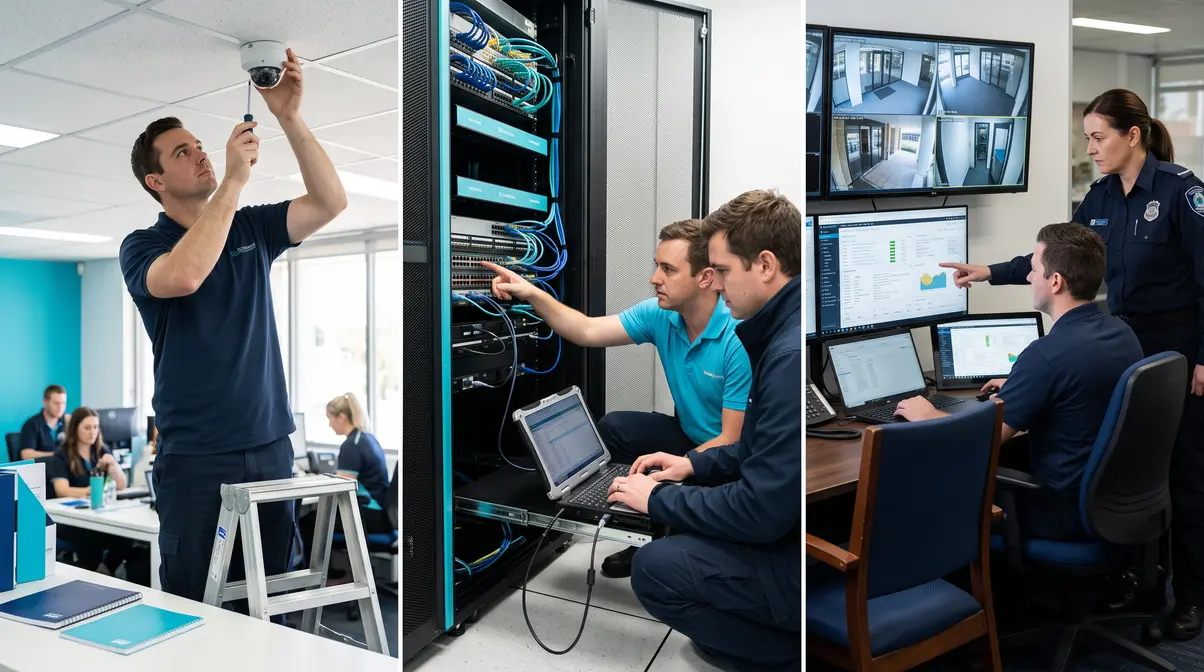
Every commercial entity operates under distinct technological conditions. A mining engineering consultancy operating in West Perth faces radically different communication risks than a logistics facility managing multi-acre yards in Henderson. Our custom in-house project training programmes bring hands-on security awareness directly into your operating environment.
Related Commercial Analysis:
Perth Vulnerability Assessments: Network & Physical Security
We work directly with your operational leaders to design tailored training modules centered around your active workflows:
- Departmental Workflows: Delivering targeted training for accounts teams handling wire authorizations, estimators receiving public tender documentation, and site supervisors using mobile devices on remote connections.
- Integrated Technology Walkthroughs: Showing staff how the physical systems around them—including network endpoints, VoIP handsets, and entrance hardware—interact with the digital network.
- Measurable Phishing Benchmarks: Measuring your workforce’s resilience over structured intervals (e.g., 30, 60, and 90-day cycles), providing commercial facility managers with real metrics on behavioral improvement and risk reduction.
Beyond Training: The Technology Layer is Non-Negotiable
Relying exclusively on staff vigilance without technical controls is a high-risk gamble. Human error is an inevitable reality in high-pressure commercial environments. True operational resilience demands that your personnel are backed by an engineered, resilient technology stack designed to drop malicious traffic before it ever lands in an employee’s inbox.
Network Infrastructure: Your First Line of Technical Defence
A poorly segmented or outdated local area network leaves an open path for attackers to move laterally. Our ICT Services team structures your infrastructure to contain threats at the edge:
- Enterprise Next-Gen Firewalls: Deployed and maintained with strict egress and ingress packet inspection rules that block outbound callbacks to known malicious infrastructure.
- Advanced Email Gateway Filtering: Utilizing behavioral heuristic scanners that quarantine suspicious zero-day domains, impersonated display names, and executable attachments before delivery.
- Automated DNS Filtering: Enforcing dynamic domain filtering across all internal switches, severing outbound links immediately if a user accidentally engages with an unverified web destination.
- Certified Structured Cabling: The physical transmission medium cannot be compromised. We build our client networks exclusively using certified Cat5E or Cat6 Ethernet cable. Substandard, non-certified cabling and degraded patch connections introduce packet drops, network instability, and security vulnerabilities that disrupt corporate controls.
Ensuring your network defenses remain updated against emerging threat models requires active technical oversight. Learn how our proactive managed IT services ensure technical defences stay hardened, patched, and monitored across the Perth metropolitan area.
The Danger of Silos: Why Your IT and Security Must Be Unified
A critical oversight we routinely identify across Perth facilities is operational separation: engaging one third-party contractor for traditional IT management and a completely separate trade contractor for physical security installations. When an intrusion happens, vendor finger-pointing follows. The IT vendor blames a compromised security appliance, while the security installer blames an unsegmented corporate network. You are left managing the fallout.
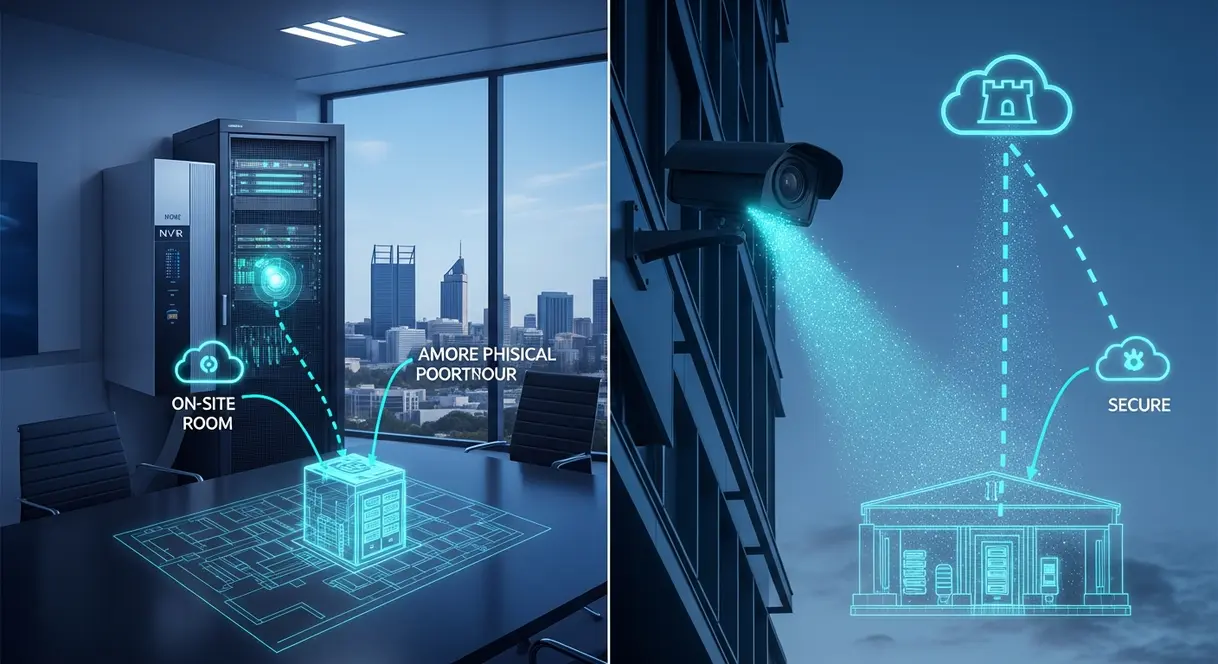
Modern electronic security equipment—specifically Commercial CCTV and Access Control systems—are networked IP endpoints running specialized operating systems. If an access panel or IP camera is installed on an unmanaged switch without proper subnetting, it creates an exposed pathway straight into your accounting and file servers. Physical security and digital network architecture can no longer be treated as isolated disciplines.
The Smart SYS Dual-Engine Model: Your Single Point of Accountability
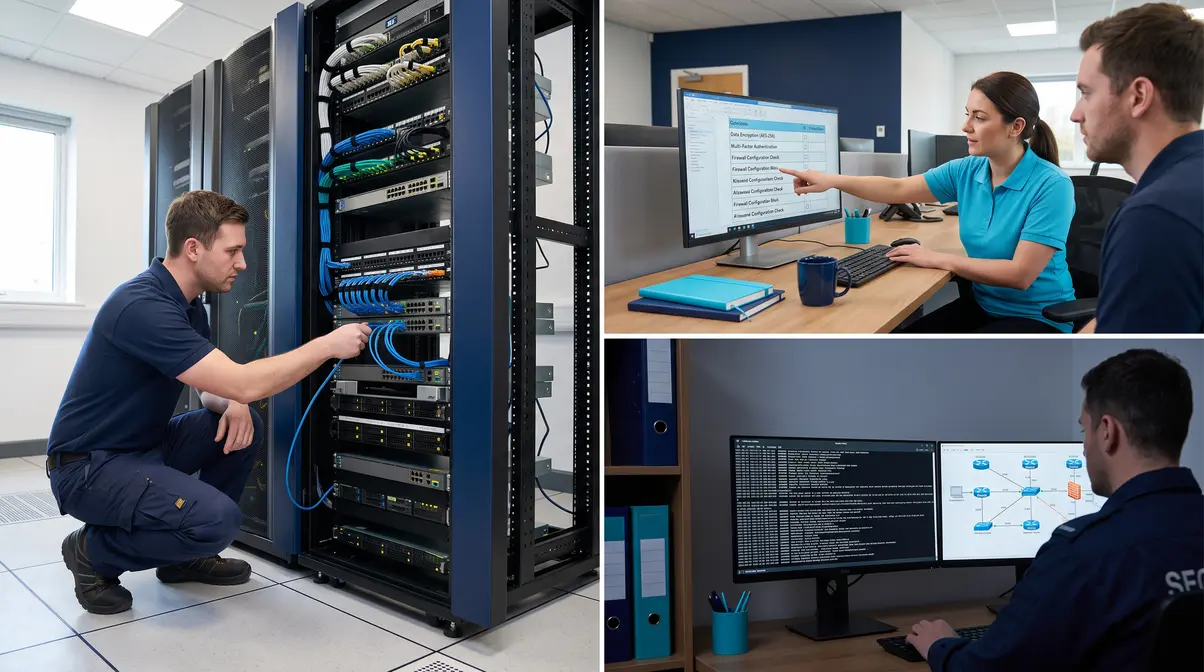
We built Smart SYS to eradicate these dangerous integration gaps. Our proprietary “Dual-Engine” model unifies dedicated ICT Services with Commercial Electronic Security under one management structure, serving as your direct Single Point of Accountability.
Integrated ICT Services
Our ICT division manages your foundational digital infrastructure: business telecommunications, VoIP PBX deployments, multi-site network links, and certified structured cabling backbones. By securing these operational layers, we assure your communication channels resist interception and social engineering tactics like executive vishing.
Integrated Security Services
Our Security Services division designs, installs, and manages Commercial CCTV, Access Control, and Commercial Alarm systems. Crucially, our engineers evaluate physical security hardware through an IT lens:
- Evidentiary-Grade Surveillance: High-quality commercial CCTV systems provide clear, evidentiary-grade footage that supports accurate incident verification and liability protection without saturating production bandwidth.
- Network Isolation & Segmentation: Every IP camera, NVR, and commercial access door controller is deployed on dedicated, access-restricted VLANs, preventing physical hardware from becoming an entry point into internal business systems.
- Master Cable Craftsmanship: Our licensed technicians manage structural installations cleanly. Whether running conduit across industrial tilt-panel masonry or threading cables through office wall cavities, we avoid building damage and maintain physical containment standards.
This joined-up approach delivers true operational defense. To learn more about unifying your vendors, explore our breakdown of the 2026 Accountability Model for Perth businesses.
Practical Steps to Defend Against Perth Phishing Attacks
Commercial business managers looking to systematically reduce phishing and lateral network risk can begin with these actionable steps:
- Evaluate Baseline Readiness: Review your current workforce education. Are simulations being run against your staff? Are critical network elements actively monitored and maintained?
- Institutionalize Dual-Authorization: Require secondary voice verification using trusted, stored contact numbers for all accounts payable updates, electronic transfers, and vendor onboarding changes.
- Enforce Modern MFA Everywhere: Mandate app-based MFA or FIDO2 hardware tokens across all software, cloud portals, and remote access gateways. Password authentication alone is no longer adequate protection.
- Simplify Incident Escalation: Ensure staff know exactly how to report suspicious emails or anomalous system prompts without fear of disciplinary blowback. Early reporting is essential for effective incident response.
- Engage an Integrated Partner: Mitigating modern cyber risks requires a unified strategy. Work with an expert provider that secures both your digital communication gateways and physical building infrastructure.
For additional guidance, review the resources published by the Australian Cyber Security Centre (ACSC) on how to Recognise and Report Phishing Attempts.
Your Best Defence is an Integrated Defence
When countering targeted phishing operations in Perth, isolated security measures will eventually break down. Standalone software licenses cannot fix weak employee awareness, and workforce training cannot prevent zero-day attacks without hardened network controls. True operational security requires an integrated strategy linking trained staff, defined incident protocols, and professionally managed infrastructure.
At Smart SYS, we architect tailored digital and physical security solutions for Perth commercial facilities. By operating as your Single Point of Accountability across ICT Services and Commercial Electronic Security, we assure there are no vendor blind spots left exposed. Contact our team to design a resilient, integrated defense system built for the modern threat landscape.
Frequently Asked Questions
Why does generic, off-the-shelf phishing awareness training often fail for Perth businesses?
Generic online training modules typically lack local and operational context. Effective defence requires continuous, context-driven simulations that mirror everyday Western Australian commercial scenarios, such as regional freight manifests, local council notices, and active supply chain workflows, rather than generic annual compliance quizzes.
How does network infrastructure support staff against phishing and malicious links?
Engineered technical controls act as an essential fail-safe when human error occurs. Next-generation firewalls, dynamic DNS filtering, and certified Cat5E or Cat6 structured cabling intercept malicious traffic at the edge, while structured VLAN segmentation helps contain lateral threat movement if credentials or endpoints are compromised.
Why should commercial electronic security and ICT systems be managed together?
Modern Commercial CCTV and Access Control systems operate as networked IP endpoints. Managing electronic security and ICT under a single point of accountability prevents security devices on unmanaged switches from becoming lateral entry points into corporate data, while eliminating vendor finger-pointing during an incident.
What immediate operational steps help prevent invoice fraud and whaling attacks?
Commercial operations should mandate out-of-band secondary verification via a known, trusted phone number before processing any vendor banking or payroll adjustments, combined with enforcing phishing-resistant Multi-Factor Authentication (MFA) across all administrative and email gateways.
Strengthen Your Perth Team Against Advanced Phishing Attacks
Equip your workforce with enterprise-grade phishing simulation training and managed email defence. Consult Perth’s licensed ICT and cyber security specialists today.
Post Comment